A protective setting is only one part of an access process. Organizations also need to handle lost devices, staff changes and a compromised administrator account without improvising under pressure.
A practical example
Choose a critical business application and walk through a fictional lost-phone case. Identify who verifies the request, which recovery method is available and how the old access is removed. Keep the procedure somewhere accessible if that application is unavailable.
What to check
- Limit privileged access and review it when roles change.
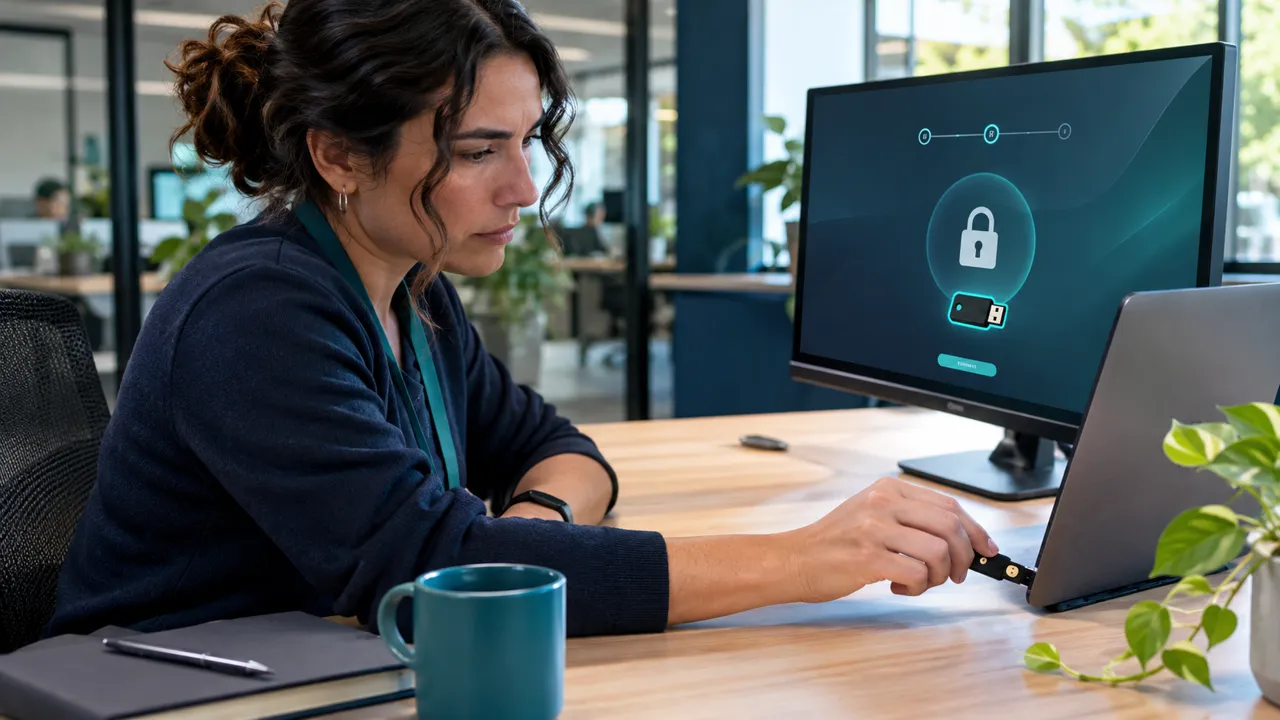
- Use appropriate strong authentication and maintain approved recovery methods.
- Assign responsibility for security alerts, updates and access removal.
The trade-off
Stronger controls should be paired with understandable support. A recovery shortcut that quietly bypasses verification can undermine the protection the organization intended to add.
Research context
CISA’s cybersecurity performance goals describe prioritized practices for organizations. They offer a baseline for planning and discussion, not a statement that completing a checklist eliminates risk.
Read the original reference material. The practical examples and evaluation questions above are TheTechGlow’s editorial application of the topic, not reported results from a product test.
Explore Cybersecurity for topic coverage, or continue to Business and Enterprise Technology for the wider sector.
References and further reading
- cisa.govhttps://www.cisa.gov/sites/default/files/2023-03/CISA_CPG_REPORT_v1.0.1_FINAL.pdf