Reference brief. This article explains published guidance and its practical context; it does not report a new launch or claim that an older source was released today.
Cybersecurity programmes need operational habits as well as products. Teams should ask how a control is maintained, how exceptions are approved and who responds when something fails. A settings screenshot cannot show whether a lost-device or departing-employee process will work.
What the source establishes
CISA’s cybersecurity performance goals describe prioritized practices for organizations. They offer a baseline for planning and discussion, not a statement that completing a checklist eliminates risk.
See the original reference material for the publisher’s scope and detail.
Questions to carry into a product or service review
- Limit privileged access and review it when roles change.
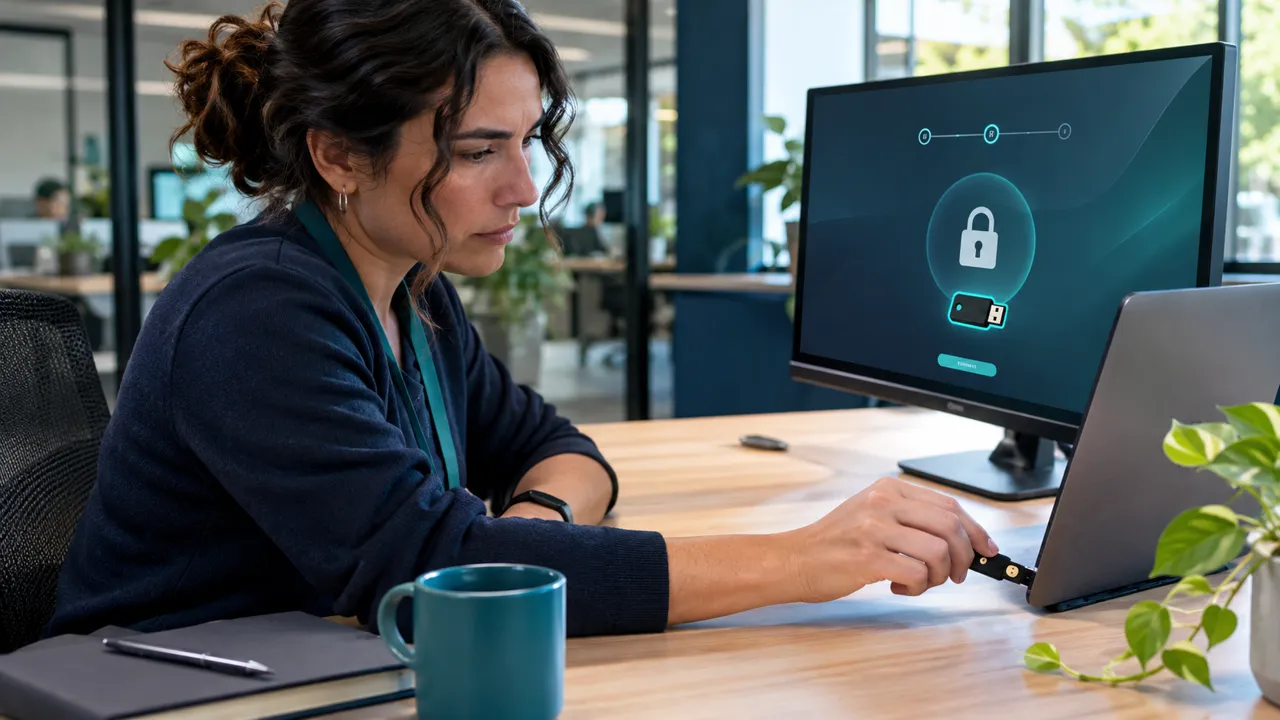
- Use appropriate strong authentication and maintain approved recovery methods.
- Assign responsibility for security alerts, updates and access removal.
Why context matters
Stronger controls should be paired with understandable support. A recovery shortcut that quietly bypasses verification can undermine the protection the organization intended to add.
For the practical example, read make account recovery part of your access-control plan. More coverage is available in Cybersecurity.
References and further reading
- cisa.govhttps://www.cisa.gov/sites/default/files/2023-03/CISA_CPG_REPORT_v1.0.1_FINAL.pdf