Reference brief. This article explains published guidance and its practical context; it does not report a new launch or claim that an older source was released today.
Agent evaluations often show the ideal path through a task. A more revealing demonstration includes a missing record, an unavailable tool and an instruction embedded in an untrusted document. The question is whether the agent preserves the intended boundary when the easy path disappears.
What the source establishes
OWASP’s agentic AI security material discusses threats and mitigations for systems that act through tools. Its security perspective helps frame testing; it does not establish business suitability on its own.
See the original reference material for the publisher’s scope and detail.
Questions to carry into a product or service review
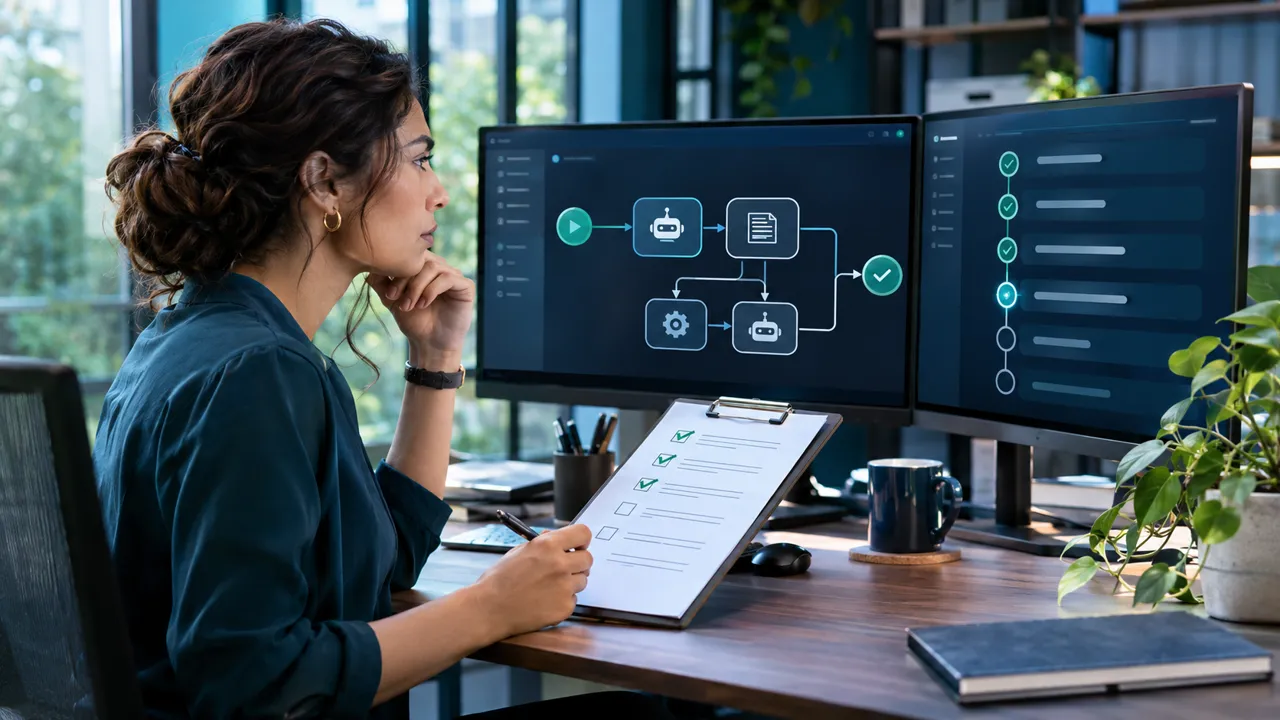
- Define which actions may run automatically and which require approval.
- Restrict tool permissions to the records and operations needed for the task.
- Make repeated failures, ambiguous identities and unexpected requests trigger a handover.
Why context matters
An extra confirmation can slow a workflow, but allowing an incorrect action can create much more work afterwards. Place approvals at meaningful decisions rather than asking for permission after every harmless lookup.
For the practical example, read give an ai agent a stopping rule before giving it another tool. More coverage is available in Artificial Intelligence Agents.
References and further reading
- genai.owasp.orghttps://genai.owasp.org/resource/agentic-ai-threats-and-mitigations/