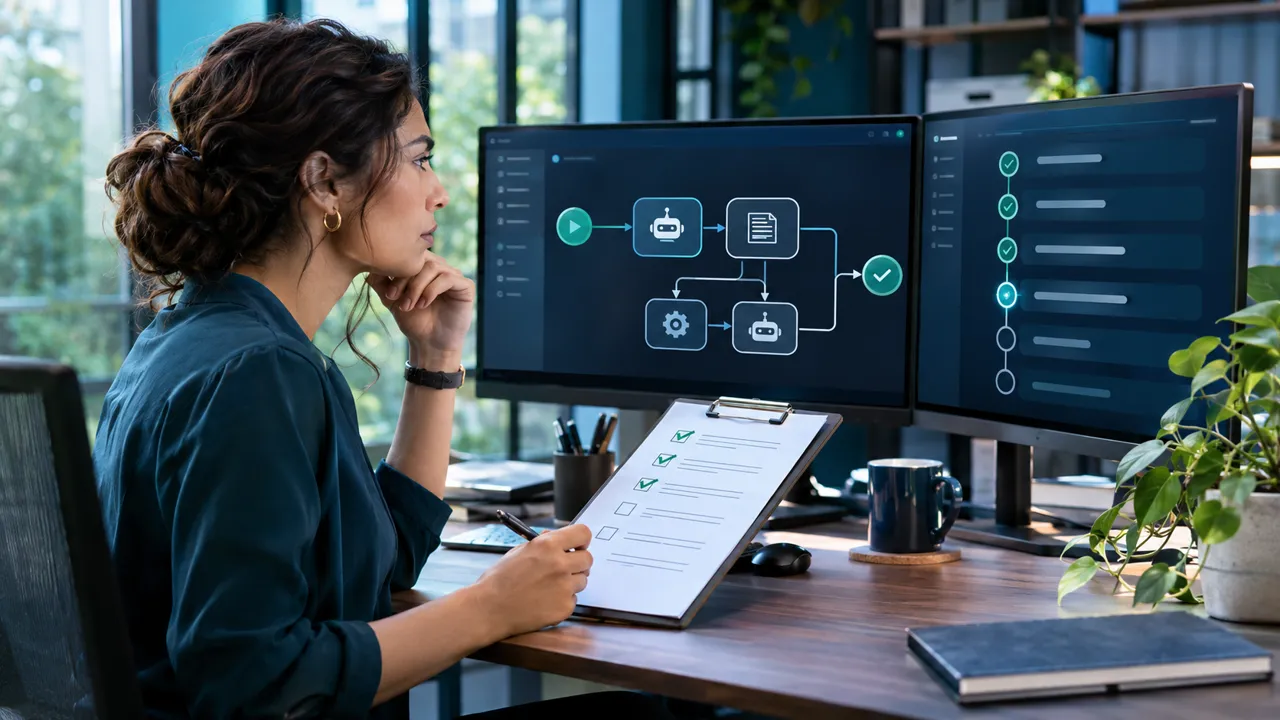
An agent becomes operationally useful when it can take a defined sequence of actions. That same ability makes its stopping rules important: uncertainty should not quietly become permission to continue.
A practical example
Consider an agent preparing a meeting booking. It may search availability and draft an invitation, but two people sharing a name should trigger a check before the invitation is sent. Test this ambiguity deliberately rather than assuming that a successful demonstration covered it.
What to check
- Define which actions may run automatically and which require approval.
- Restrict tool permissions to the records and operations needed for the task.
- Make repeated failures, ambiguous identities and unexpected requests trigger a handover.
The trade-off
An extra confirmation can slow a workflow, but allowing an incorrect action can create much more work afterwards. Place approvals at meaningful decisions rather than asking for permission after every harmless lookup.
Research context
OWASP’s agentic AI security material discusses threats and mitigations for systems that act through tools. Its security perspective helps frame testing; it does not establish business suitability on its own.
Read the original reference material. The practical examples and evaluation questions above are TheTechGlow’s editorial application of the topic, not reported results from a product test.
Explore Artificial Intelligence Agents for topic coverage, or continue to Artificial Intelligence & Automation for the wider sector.
References and further reading
- genai.owasp.orghttps://genai.owasp.org/resource/agentic-ai-threats-and-mitigations/